Senior IT Architect & Information Security Professional
Building secure, scalable systems for modern enterprises
25+ years of enterprise technology experience bridging operational IT and defensive security. Expert in SIEM/SOAR/XDR/EDR architecture, Elastic Stack security operations, and large-scale automation. Author of a published Cyber Law and Governance analysis of CVE-2025-59145 (CamoLeak). Co-founder & CTO of Cynipol Systems.
Core Focus Areas
Deep expertise across security architecture, systems engineering, and enterprise operations.
Security Architecture
SIEM/SOAR/XDR/EDR design, Elastic Stack operations, IAM/OIM triage, threat countermeasures, and compliance frameworks (HIPAA, ITAR, PCI DSS).
Systems & Endpoint Engineering
Large-scale MECM/SCCM imaging, Windows Server & Linux administration, Active Directory, PowerShell/BASH automation, and ITIL-aligned ITSM platforms.
Platform Development
Co-founder & CTO of Cynipol Systems — enterprise SaaS for ITSM, Security (SIEM/SOAR), HR, Projects, Events, and Business Operations with deep compliance mapping.
Featured Project
Cynipol Systems
Enterprise Operations Platform integrating ITSM, SIEM/SOAR, HR, Project Management, Event Management, Financials, and Student Information Services. It began as the capstone for my MS IT at Southern New Hampshire University; once the work was under way, the capstone was narrowed to the Vulnerability Intelligence pipeline within Cynipol Security, and the platform continues to grow as a full multi-module suite.
- ▸ ITSM with ticketing, asset lifecycle, KB, and SLA automation
- ▸ Security module with compliance mapping (ISO 27001, NIST CSF, HIPAA, PCI DSS, SOX…)
- ▸ HR, Timesheets, Skills & Training, Events, and Financial reporting
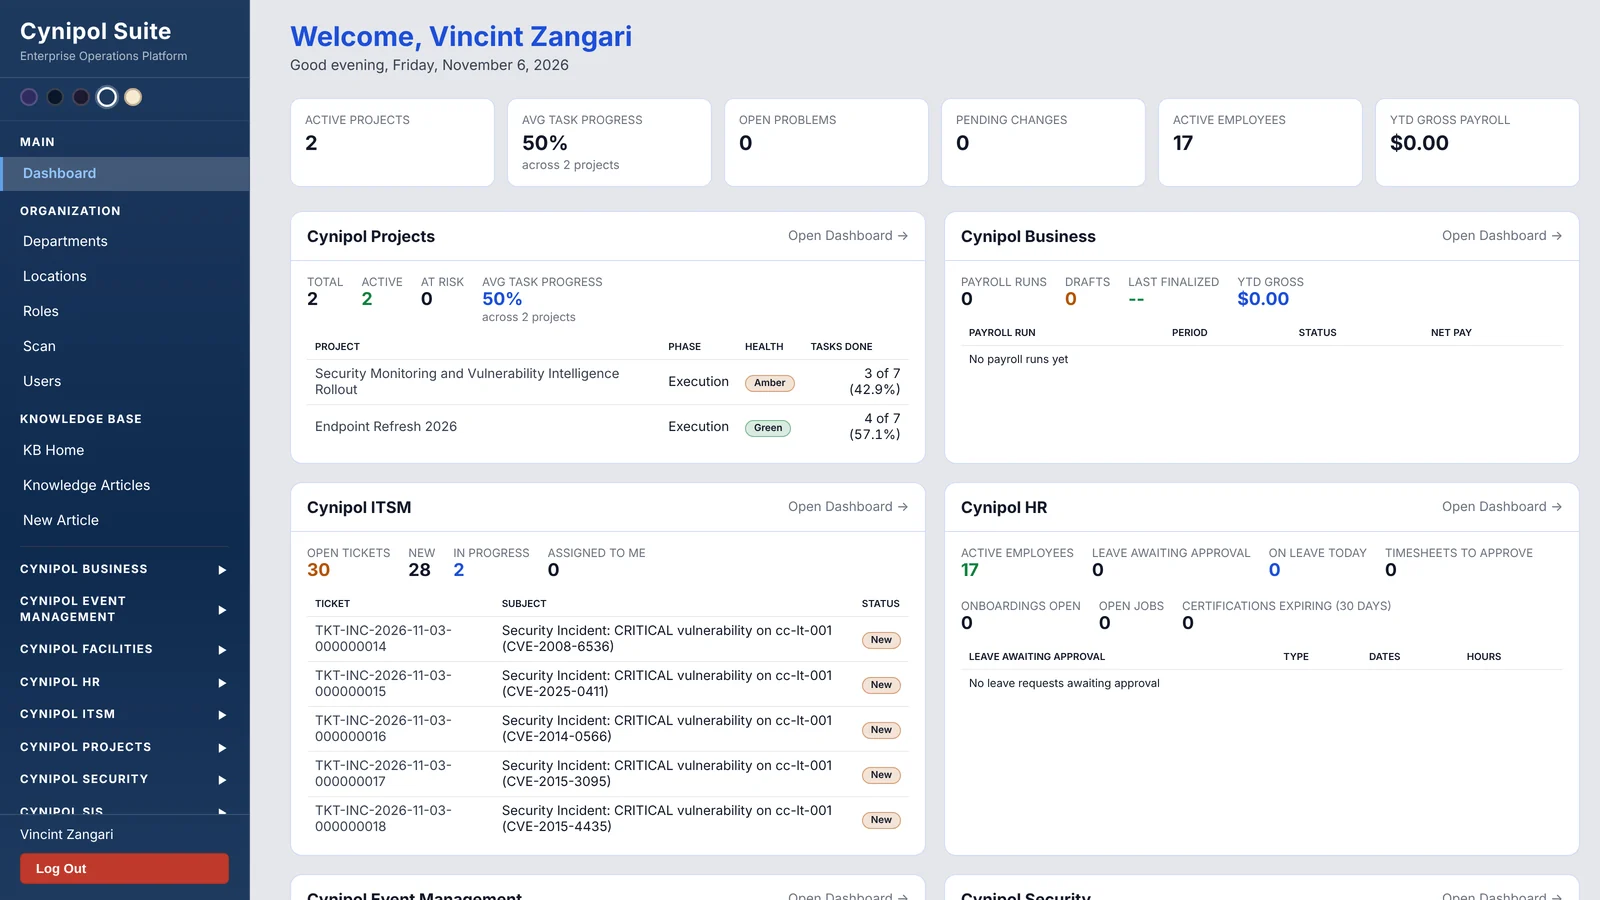
The Cynipol Suite dashboard, shown with demo data for C Corp
Independent Security Research
CVE-2025-59145 — CamoLeak
Published Cyber Law and Governance analysis of CVE-2025-59145, a CVSS 9.6 prompt injection vulnerability in GitHub Copilot, and of the sixty-day silent remediation window that left 100M+ developers unaware of it. Demonstrates ongoing commitment to vulnerability research and defensive security beyond operational roles.
Read the analysis →Let’s connect
Interested in architecture reviews, security assessments, or collaboration? Request a copy of my resume or reach out directly.
Request Resume